What Is Infrastructure as Code (IaC)? A Business Owner’s Plain-English Guide
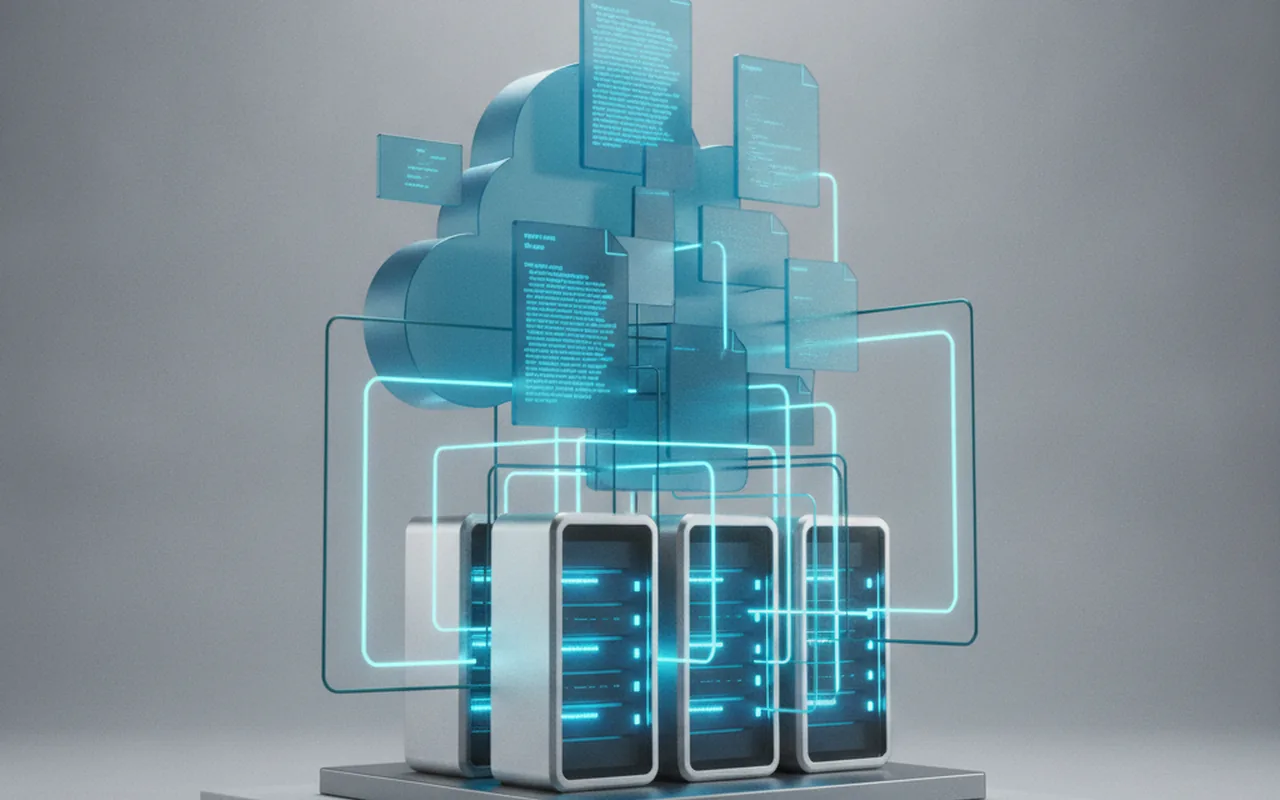
TL;DR: Infrastructure as code (IaC) means defining servers, networks, and databases in version-controlled configuration files instead of clicking buttons in a cloud console by hand. Teams write the setup once, store it like application code, and run it automatically to build identical environments every time — cutting manual errors, speeding up deployments, and making every change reviewable before it ships.
If you have ever asked your development team why a feature that works perfectly in testing breaks the moment it reaches production, the answer is often buried in how the servers underneath that feature were set up. For decades, infrastructure was configured by hand: an engineer logged into a console, clicked through menus, and provisioned a server, a database, and a network rule one step at a time. Repeat that process on a second environment and small inconsistencies creep in — a missing setting here, a different version there — until no two environments are quite the same.
Infrastructure as code replaces that manual ritual with a written definition of the infrastructure itself, checked into the same version control system that already governs your application code. When your team builds a product through a custom software development team that treats infrastructure this way from day one, the environment a customer runs in production is provably identical to the one your engineers tested against — because it was generated from the same file.
This guide explains what infrastructure as code actually is, why it matters to your business even if you never touch a terminal, and what to ask your team or vendor to find out whether they are really doing it.
What Is Infrastructure as Code, in Plain English?
Think of infrastructure as code the way you would think of a recipe versus cooking from memory. Cooking from memory means every attempt is slightly different — a pinch more salt one day, a few minutes longer in the oven the next. A written recipe, by contrast, produces the same dish every time, can be handed to someone else, and can be reviewed and improved before anyone cooks with it again.
Infrastructure as code is that recipe for your servers, networks, storage, and databases. Instead of an engineer manually clicking through a cloud provider’s dashboard to create a server, a load balancer, and a firewall rule, the entire setup is written in a configuration file — a precise, machine-readable description of what the infrastructure should look like. Running that file against a cloud provider produces the exact environment described, every single time, whether it is the first run or the hundredth.
Because the configuration lives in a file rather than in someone’s memory of what they clicked, it can be stored in version control (the same system, usually Git, that tracks every change to your application’s code), reviewed by a second engineer before it takes effect, and rolled back instantly if something goes wrong. That is the core shift: infrastructure stops being a one-off manual task and becomes a reviewable, repeatable artifact — just like code.
Why Does Infrastructure as Code Matter for Your Business?
You do not need to understand Terraform syntax to care about IaC. You need to care about what it changes for your business, which comes down to five concrete outcomes.
- Consistency. Every environment — development, staging, production — is built from the same definition, eliminating the “it works on my machine” class of bug that costs engineering hours to track down.
- Speed. Spinning up a new environment goes from a multi-day manual checklist to a single automated run that takes minutes, which matters directly when you are scaling for a launch or recovering from an outage.
- Error reduction. A report from Splunk’s State of Security research has repeatedly found that human error and misconfiguration are implicated in the vast majority of security incidents; removing manual console clicks from the provisioning process removes the single biggest source of that risk.
- Cost control. Because the exact infrastructure footprint is defined in a file, it is far easier to see — and delete — resources nobody is using anymore, instead of discovering forgotten servers on next month’s cloud bill.
- Auditability. Every change to the infrastructure is a commit with a timestamp and an author, giving you a complete, searchable history of who changed what and why — valuable for compliance reviews and incident investigations alike.
How Does Infrastructure as Code Actually Work?
Underneath the concept, IaC follows a consistent four-step workflow regardless of which tool a team uses.
Write
An engineer describes the desired infrastructure — a database, a web server, a network rule — in a configuration file using the syntax of a specific IaC tool. This step replaces the manual clicking with a declaration of what should exist.
Version
That configuration file is committed to the same Git repository that holds the application’s source code, or a closely related one. From this point on, every change to the infrastructure goes through the same pull-request review process as a code change — a second engineer reads the diff before it is approved.
Provision
Automated tooling reads the configuration file and creates, updates, or removes the actual cloud resources to match it. The engineer never logs into the cloud console directly; the tool does the provisioning based solely on what the file says.
Deploy
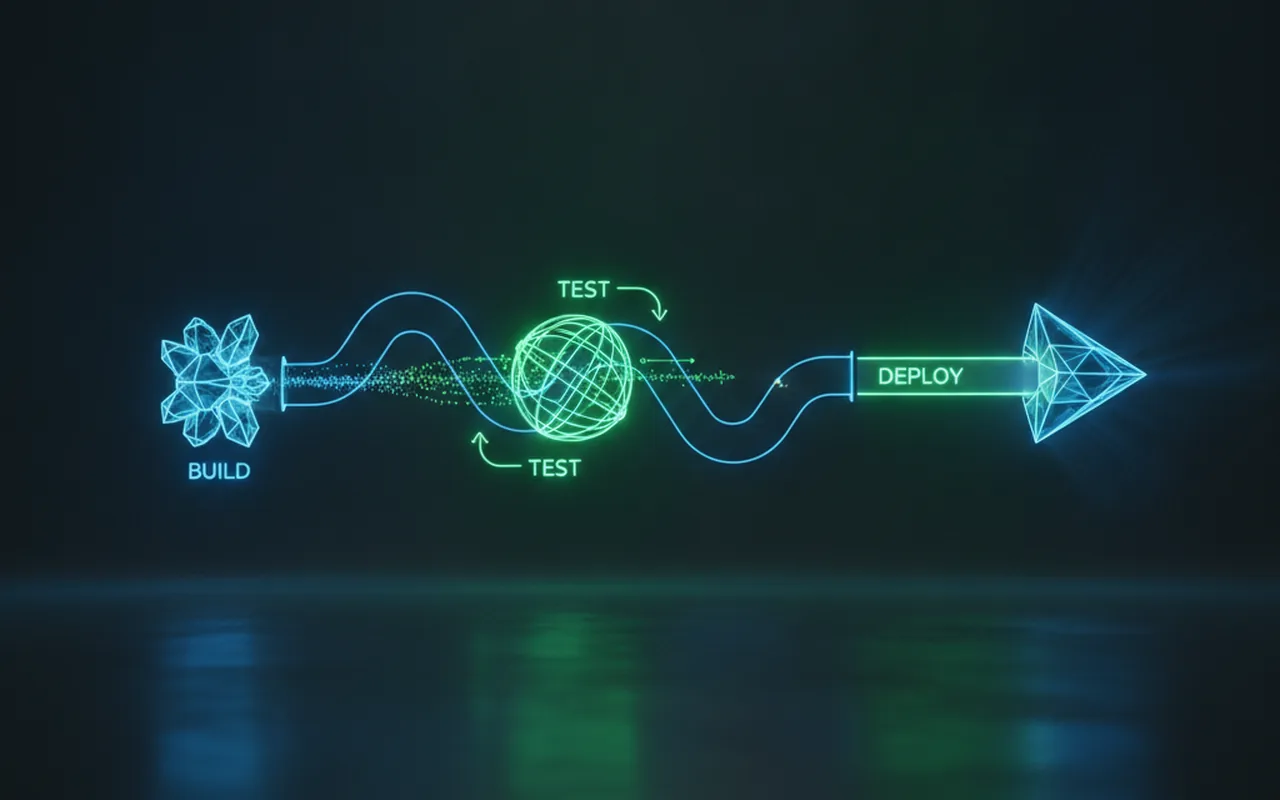
The same automated pipeline that ships application code — the CI/CD pipeline — runs the infrastructure provisioning step alongside the application deployment, so the environment and the application that runs on it are always updated together, not as two separate, easy-to-desync processes.
Declarative vs. Imperative: The Two Approaches to IaC
Every IaC tool follows one of two philosophies for describing infrastructure, and the difference matters when you are evaluating which approach your team should use.
A declarative approach describes the desired end state — “I want three web servers and one database” — and leaves it to the tool to figure out the steps needed to get there, whether that means creating new resources or changing existing ones. An imperative approach instead lists the exact sequence of commands to run — “create a server, then create a database, then connect them” — in the order they must execute.
| Dimension | Declarative | Imperative |
|---|---|---|
| What you write | The desired end state | The exact steps to reach that state |
| Who figures out the “how” | The tool | The engineer |
| Re-running it is safe | Yes — the tool only changes what differs (idempotent) | Only if the script was written to check current state first |
| Readability for non-authors | Higher — reads like a description of the environment | Lower — requires tracing execution order |
| Common tools | Terraform, AWS CloudFormation, Pulumi (declarative mode) | Ansible playbooks, shell/Python provisioning scripts |
Most modern teams favor declarative tools such as Terraform or AWS CloudFormation for provisioning cloud resources, because the tool’s ability to compare the desired state against what currently exists — and change only the difference — makes re-running the same configuration safe. That property is called idempotency, and it is one of the main reasons IaC is more reliable than manual provisioning: running the same file twice produces the same result, not a second set of duplicate resources.
Mutable vs. Immutable Infrastructure — Why It Matters
A related distinction your team may bring up is mutable versus immutable infrastructure. With mutable infrastructure, an existing server is updated in place — patched, reconfigured, upgraded — which over time can drift from its original definition in small, hard-to-trace ways. With immutable infrastructure, a server is never modified after it is created; instead, a change means building a brand-new server from the updated configuration and replacing the old one entirely.
Immutable infrastructure is generally considered the safer default for IaC-managed environments, because it eliminates configuration drift entirely — the running server always matches its definition exactly, since nothing was ever changed by hand after the fact.
What Tools Do Teams Use for Infrastructure as Code?
The IaC tooling landscape has consolidated around a handful of well-established options, each suited to a different situation.
| Tool | Type | When it’s the right fit |
|---|---|---|
| Terraform | Declarative, multi-cloud | You use more than one cloud provider, or want to avoid vendor lock-in |
| AWS CloudFormation | Declarative, AWS-native | You are fully committed to AWS and want deep native integration |
| Azure Resource Manager (ARM) | Declarative, Azure-native | Your infrastructure lives primarily on Microsoft Azure |
| Pulumi | Declarative, general-purpose languages | Your team wants to write infrastructure in Python, TypeScript, or Go instead of a dedicated syntax |
| Ansible / Puppet / Chef | Primarily configuration management | You need to configure software on existing servers, not just provision new ones |
Many teams combine two tools: one for provisioning the raw infrastructure (Terraform or CloudFormation) and one for configuring the software that runs on it (Ansible) — a pairing documented in Red Hat’s overview of IaC.
How Does IaC Fit Into DevOps and CI/CD?
Infrastructure as code is one of the foundational practices of DevOps — it is the piece that lets infrastructure move at the same speed as application code instead of lagging behind it as a separate, manual process. Without IaC, a CI/CD pipeline can automate testing and deploying application code all day long, but the servers that code runs on still have to be configured by hand somewhere — which reintroduces exactly the inconsistency and risk that CI/CD was built to eliminate.
With IaC in place, the infrastructure definition sits in the same repository and travels through the same pipeline as the application. A pull request that changes a server’s memory allocation gets reviewed the same way a pull request that changes a line of application code does, and both are deployed together, keeping the application and the environment it depends on permanently in sync.
What Challenges Should You Expect When Adopting IaC?
IaC is not free of trade-offs, and knowing the common friction points helps you set realistic expectations with your team.
- Learning curve. Writing infrastructure as code requires engineers to learn a new syntax and a new mental model, even if they are already comfortable writing application code.
- State file management. Declarative tools like Terraform track the current state of your infrastructure in a file that must be stored and protected carefully — losing or corrupting it can make the tool lose track of what it is managing.
- Configuration drift. If someone makes a manual change outside the IaC process — even a small one, in an emergency — the real infrastructure no longer matches the file, and the next automated run can behave unpredictably until the drift is reconciled.
- Access and permissions. Because the IaC tool now has the power to create and destroy real infrastructure, who can approve and run those changes becomes a serious access-control question, not an afterthought.
None of these are reasons to avoid IaC — they are reasons to introduce it deliberately, with code review and limited deployment permissions in place from the start, rather than retrofitting discipline after an incident.
Is Infrastructure as Code Right for Your Project?
IaC pays off fastest on projects with more than one environment to keep in sync, infrastructure that changes more than occasionally, or a team large enough that “ask the one person who remembers how the server is set up” is no longer a workable process. A few signals it is time:
- You run separate development, staging, and production environments and they have quietly drifted apart.
- You are using — or planning to use — container orchestration such as Kubernetes, which almost always sits on top of infrastructure that is itself provisioned through IaC, since a Kubernetes cluster has far too many moving parts to configure reliably by hand.
- Standing up a new environment currently takes days of manual setup instead of minutes.
- A single engineer leaving would leave the team unsure how production infrastructure is actually configured.
If your project is a single small server that rarely changes, the overhead of adopting a full IaC toolchain may outweigh the benefit — but almost any product expected to scale, or any team larger than one or two engineers, will outgrow manual provisioning faster than expected.
Frequently Asked Questions
Is Infrastructure as Code only for large companies?
No. Small teams often benefit the most, because they have the least capacity to absorb the time lost to manually rebuilding an environment after something breaks, and the fewest people available to be the sole holder of undocumented infrastructure knowledge.
Do I need to learn to code to use IaC?
You personally do not — this is a practice for your engineering team, not something a business owner implements directly. Declarative IaC languages are also deliberately closer to structured configuration than to traditional programming, which makes them faster for engineers to learn than a general-purpose language.
What’s the difference between IaC and configuration management?
Infrastructure as code typically refers to provisioning — creating the servers, networks, and databases in the first place. Configuration management refers to keeping the software on those servers correctly configured over time. In practice teams often use two tools together: one (like Terraform) to provision, and one (like Ansible) to configure.
How much does it cost to adopt Infrastructure as Code?
The tools themselves (Terraform, Ansible, and most cloud-native options) are free and open source; the real cost is engineering time to write the initial configuration and the learning curve for the team. Most teams recoup that investment within a few months through faster environment setup and fewer production incidents caused by configuration drift.
Can Infrastructure as Code work with an existing (non-cloud-native) setup?
Yes, though it usually happens gradually. Teams typically start by writing IaC definitions for new infrastructure going forward, then incrementally “import” existing servers into the IaC tool’s management as time allows, rather than rewriting an entire production environment in one risky step.
Infrastructure as code will not show up in a product demo, and most customers will never know it exists. What they will notice is a product that stays up during traffic spikes, ships new features without weekend-long deployment incidents, and recovers quickly when something does go wrong — all of which trace back to infrastructure that is defined, reviewed, and reproducible, rather than remembered.